We ended the last episode with some brief considerations on notification obligations. Let’s now take a look at the risks involved in being caught unprepared for the actual enforcement of the NIS 2 Decree.
Increasing economic sanctions
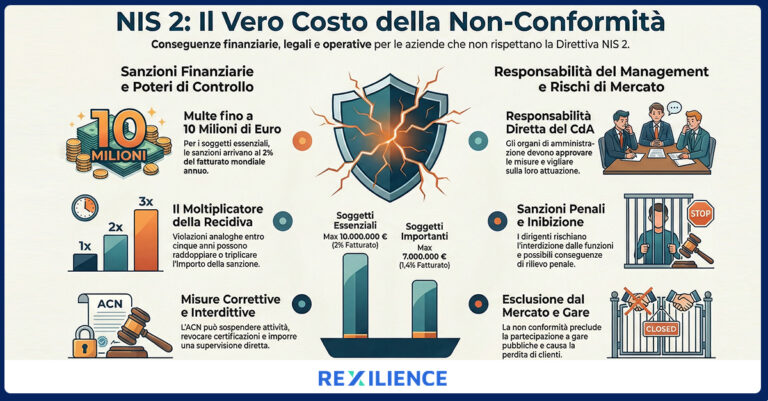
The penalties are severe. For key players, fines can reach up to €10 million or 2% of global annual turnover; for major players, up to €7 million or 1.4%.
The recidivism mechanism provides for significant aggravations: similar violations within five years can lead to doubled or tripled penalties.
In short, these are not exactly light or “symbolic” sanctions.
Direct responsibility of administrative bodies
The ACN Determination of April 14, 2025, subsequently updated and replaced by No. 379907 of December 19, 2025, clarifies that cybersecurity is the responsibility of the administrative bodies. The Board of Directors and sole directors must formally approve security measures, but not only that, they must also allocate resources and oversee implementation. In the event of non-compliance, temporary suspension from management functions and even criminal liability of the Executive Committee are possible.
Disqualification measures and additional penalties
In addition to financial penalties and disqualifications, the ACN may impose corrective measures under direct supervision, suspend activities related to cybersecurity, revoke certifications or authorizations, and apply periodic penalties until the situation is restored in accordance with the Decree and secondary legislation.
Market exclusion and competitive disadvantage
Non-compliance can prevent participation in public tenders, cause the loss of customers, and, above all, damage reputation. If the main driver for many organizations is always revenue and competitiveness, any sanctions can only have a devastating effect on the business continuity of these entities.
Clearly, there are also other significant penalties, multiple repercussions to consider, and hidden operational dysfunctions; let’s say that these are the main ones to weigh up in the event of non-compliance.
But what about all those who are late? Let’s talk about that for a moment…
Signs that indicate you are not ready
There are clear indicators of unpreparedness, not only formal ones (such as the absence of mere documentary evidence): usually, the degree of maturity (which can be measured in many ways) involves the organizational, technological, physical, and even personnel aspects. In fact, if we really wanted to use a scale we are familiar with, we could use the one used by the NIS 2 Decree in terms of governance and security measures. The ingredients for our compliance recipe are all on the table.
But what about all those who are late?
We will discuss them briefly in the next episode.