ISO/IEC 27001: the internal audit that demonstrates the effectiveness of controls
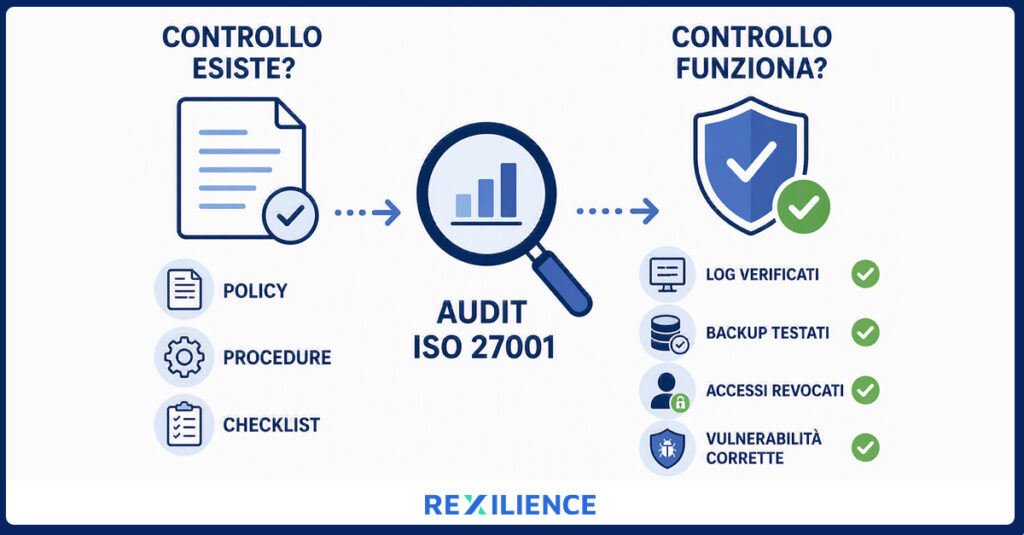
ISO/IEC 27001: the internal audit that demonstrates the effectiveness of controls From testing to non-conformities: how to make the management review effective. There is a misconception associated with many information security management systems: viewing the internal audit as a mere paperwork exercise, to be carried out once a year to ensure the organisation is prepared […]